

Astonishingly, the private keys were 4, 56, 66, 115, 155, 156, 230, 237.
exploiting compromised certificates requires an active adversary-in-the-middle attack, meaning the attacker must act as a proxy between two TLS parties and receive encrypted traffic, decrypt it, reencrypt it, and send it to the other party. Such capabilities, in some cases, are usually limited to only the most well-resourced attackers. People with control of a local network—at a coffee shop, university, or other organization—face much less of a challenge.
https://emudhra.we-have-a-problem.com/
I think that this isn’t really getting the right attention, about what a massive WTF situation this is…
its a 384 bit certificate and this is the private key
00:00:00:00:00:00:00:00:00:00:00:00:00:00:00:
00:00:00:00:00:00:00:00:00:00:00:00:00:00:00:
00:00:00:00:00:00:00:00:00:00:00:00:00:00:00:
00:00:04
that is just fucking NUTS
Phew to think how close it is to my private key
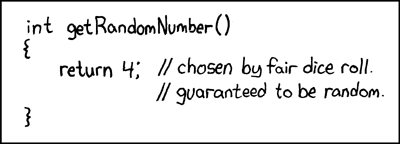
that’s a very long way to spell the random number 4
::4
That kind of removes the bit size and hides it in assumption.
And 8 of them no less. The guess of this being test code leaking into prod is likely, but security focused companies need consequences for stuff like this. That being said:
Looks like consequences to me…
It’s like winning the lottery
Winning the lottery is (ballpark) 1 in 10^9, so generating a key below a million is like winning 11 lotteries in a row, while buying 1 ticket in each.
They wouldn’t know how you’d done it, but I think you’d be arrested, with valid probable cause.
is much more secure.
LOL, People are never gonna give this up.
I’m too lazy to do the math. Does that translate to the URL?
No, it is a string of text. “Never gonna give you up never gonna let you down”
"Never gonna give you up never gonna let you down "
ROFL, People are never gonna let this down.
I mean, yes, it’s entirely possible and within the realm of probability of getting that as a key. But realistically it’s very, very, fucking unlikely.
Ye, I’d struggle to believe ONE key getting generated like that, but 8 points to pure incompetence
Isn’t every key equally unlikely?
Yes, be in is why having 8 of them total in the 2 digit range (I.e only using up to 6 bits of 384-bits) just screams incompetence of a hand generated key.