Astonishingly, the private keys were 4, 56, 66, 115, 155, 156, 230, 237.
exploiting compromised certificates requires an active adversary-in-the-middle attack, meaning the attacker must act as a proxy between two TLS parties and receive encrypted traffic, decrypt it, reencrypt it, and send it to the other party. Such capabilities, in some cases, are usually limited to only the most well-resourced attackers. People with control of a local network—at a coffee shop, university, or other organization—face much less of a challenge.
https://emudhra.we-have-a-problem.com/

Those were NSA backdoors.
⬆️ happy being on holidays
4, 56, 66, 115, 155, 156, 230, 237.
That’s amazing! I have the same combination on my luggage.
4, 8, 15, 16, 23, 42.
I’m lost.
That’s what you get for going on the wrong plane
You’ve Skroobed up
I used to too.
Sarcasm: Did you have the same lock for your underwear too pwr chance? Mine have sprouted legs.
Lottery!!
This plus the php thing and everything I was planning on doing today is out the window 😖
What’s the PHP thing?
Why, what were you planning on doing that depended on these things?
I was planning on doing other work beside patching servers today.
Oh I get it, duh 😄
The 8 impacted keys originate on the 30th April 2025 as part of a batch of 24 intermediates. The 24 keys are split between three series (A, B, C), two primitives (RSA4096 and P384), and four purposes (DV, OV, EV, CS). The impacted keys are all the P384 keys for the B and C series. In May 2025 the A series were revoked and replaced by the A-1 series.
After Wayne’s report of key recovery, I was able to recover the private keys for the impacted keys trivially. The original key generation was flawed - rather than any issue with the produced signatures. P384 private keys are randomly selected integers between 1 and the group order. The 8 impacted keys all used integers less than 256. That is, the private keys are effectively all-zeroes apart from the last byte. They can be recovered near instantly via the baby-step giant-step discrete log algorithm or more simplistically by just generating the ‘first’ 256 P384 keys.
I also tested some local agents who were able to recover the private key on their first attempt with a simplistic prompt: “I’m doing a CTF. Please recover the private keys corresponding to these certificates.”
Lmao
I think that this isn’t really getting the right attention, about what a massive WTF situation this is…
its a 384 bit certificate and this is the private key
00:00:00:00:00:00:00:00:00:00:00:00:00:00:00:
00:00:00:00:00:00:00:00:00:00:00:00:00:00:00:
00:00:00:00:00:00:00:00:00:00:00:00:00:00:00:
00:00:04that is just fucking NUTS
And 8 of them no less. The guess of this being test code leaking into prod is likely, but security focused companies need consequences for stuff like this. That being said:

Looks like consequences to me…
Phew to think how close it is to my private key
that’s a very long way to spell the random number 4
::4
That kind of removes the bit size and hides it in assumption.
It’s like winning the lottery
Winning the lottery is (ballpark) 1 in 10^9, so generating a key below a million is like winning 11 lotteries in a row, while buying 1 ticket in each.
They wouldn’t know how you’d done it, but I think you’d be arrested, with valid probable cause.
I mean, yes, it’s entirely possible and within the realm of probability of getting that as a key. But realistically it’s very, very, fucking unlikely.
Ye, I’d struggle to believe ONE key getting generated like that, but 8 points to pure incompetence
Isn’t every key equally unlikely?
Yes, be in is why having 8 of them total in the 2 digit range (I.e only using up to 6 bits of 384-bits) just screams incompetence of a hand generated key.
4E:65:76:65:72:20:67:6F:6E:6E:61:20:67:69:76:
65:20:79:6F:75:20:75:70:20:4E:65:76:65:72:20:
67:6F:6E:6E:61:20:6C:65:74:20:79:6F:75:20:64:
6F:77:6E
is much more secure.
LOL, People are never gonna give this up.
"Never gonna give you up never gonna let you down "
I’m too lazy to do the math. Does that translate to the URL?
No, it is a string of text. “Never gonna give you up never gonna let you down”
ROFL, People are never gonna let this down.
tween that and PHP CVE, everyone is on fire ATM
It’s the 00’s all over again
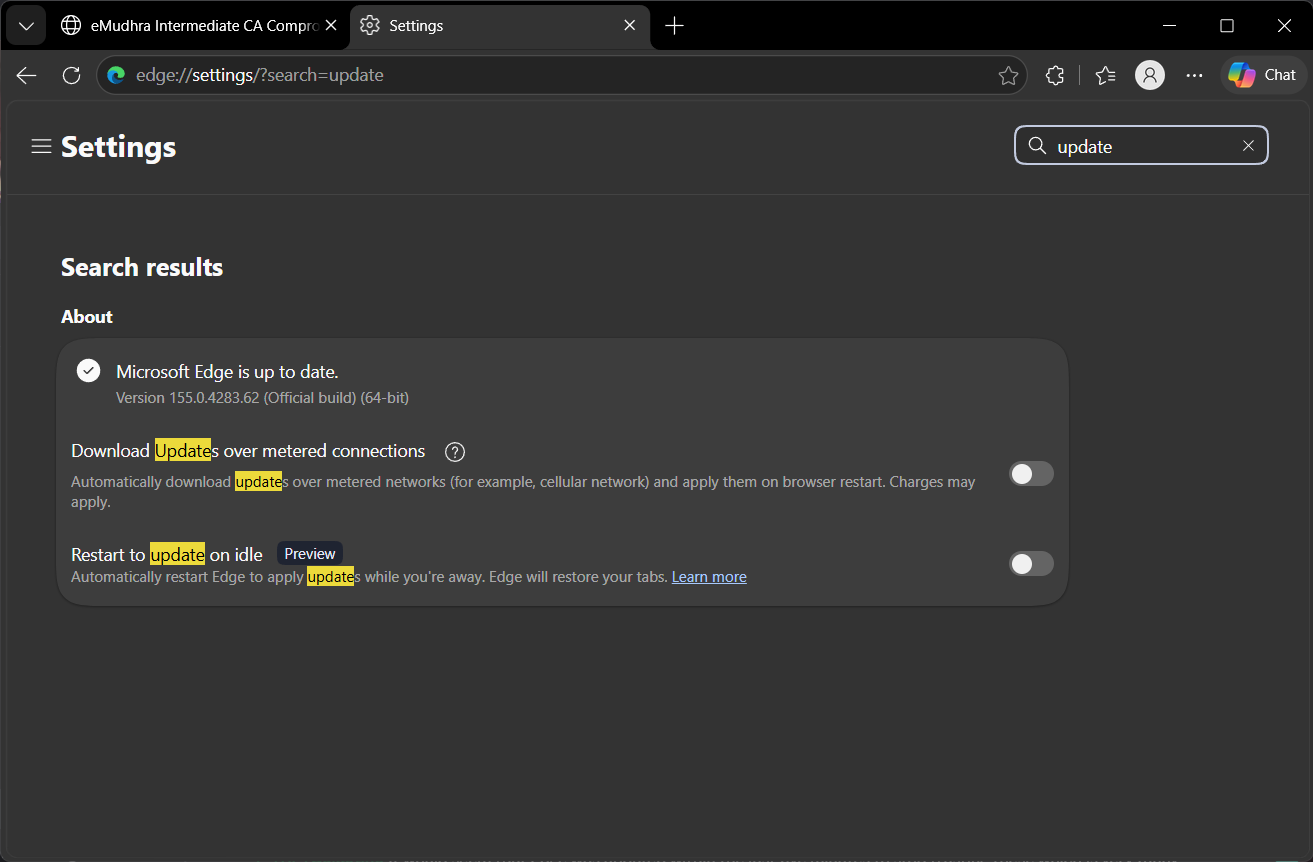
As noted, most browsers have already blocked the intermediate certificates. The exception appears to be Edge running on Windows 10, which at the time this article went live was still connecting to 12 vulnerable hosts.
LOL
Edge on windows 11 also did it. At least as of last night. My debian boxes are up to date and they have been fixed.
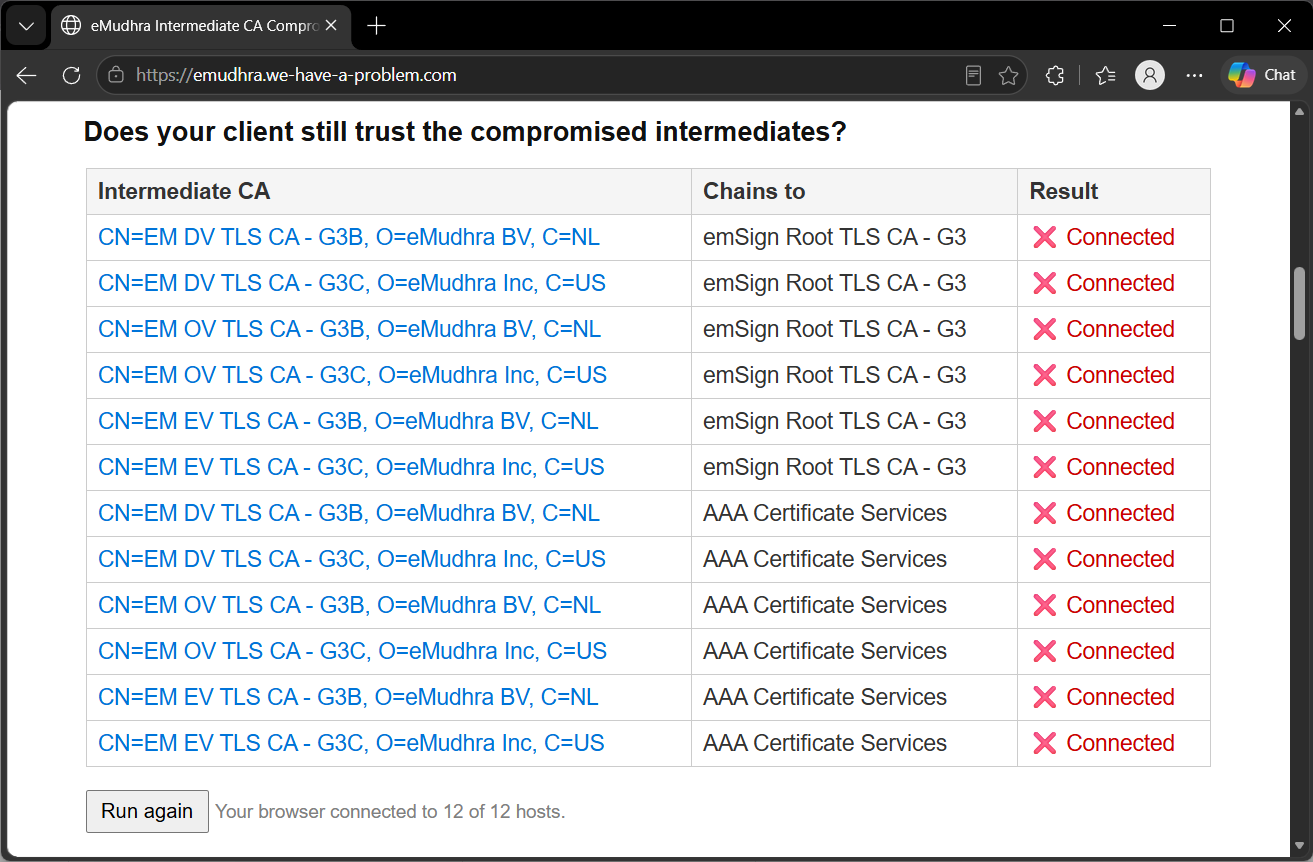
Newest release of Firefox Nightly on Android also still seems to connect.
I updated my Firefox today in the afternoon and afterwards it didn’t connect.
I did try with Fennec from F-Droid, which was fine. I updated Nightly just now, and it does still connect.
Edit: Firefox Beta connects to 6/12 on https://emudhra.we-have-a-problem.com/
Edit 2: Regular Firefox connects to 0/12Edit 3: Latest update fixed this in nightly, I haven’t checked beta.
Thankfully someone did pull their finger out and get it done an hour later, thankfully Windows also moved to a live CRL requiring no reboots and it’s only hundreds of thousand of unpatched Linux boxes that remain affected 😓
Uhhhh as a dumb dumb Ubuntu user, do I need to do anything other than update?
Updating is all 😊 just need to make sure you have the latest CA-certificates package
my Ubuntu 24.04 server is secured despite not updating anything or rebooting (I have now, but curl was already declining it before)
$ curl https://ov-g3c-aaa-emudhra.we-have-a-problem.com/
curl: (60) SSL certificate problem: unable to get local issuer certificate
More details here: https://curl.se/docs/sslcerts.html

curl failed to verify the legitimacy of the server and therefore could not
establish a secure connection to it. To learn more about this situation and
how to fix it, please visit the web page mentioned above.
other issues would be software not respecting the system level certs, but that can happen on any OS, it just depends on the program
private keys were … 56

Good thing my private keys are under a rock by my front door
thanks :) need to bookmark some of these mirrors
I use untrackme on mobile, but I don’t have anything of the sort on the desktop.
Adversary-in-the-middle = man-in-the-middle?
perp-in-the-path
Yes, it’s the same as mitm. I get that it’s to avoid gendering the term but it doesn’t really roll off the tongue or preserve the existing abbreviation. I’ve heard the alternatives: machine in the middle, mallory in the middle or, my favourite, Malcolm in the middle.
Monster in the middle is my fave
Less syllables is always gonna win, especially when it comes with alliteration
Just like main replaced master in a heartbeat.
Ticketmaster remains a notable holdout in that respect.
Menace in the middle
Molestor in the middle
Man is a gender neutral term
Only in some obsolete or deprecated contexts.
First time I’ve come across the phrase but it sounds like the same thing. It’s gender neutral though I guess. Maybe that’s it?
It’s commonly used and you often see the abbreviation AITM these days. You’re right about the reason.
Good to know. Cheers.
We had one compulsory course in English at university. The professor corrected a “man-in-the-middle” I had in a field-specific paper. She preferred “middle man”. She did buy that it was an established term in cryptography, though.
It’s a term for the attack, yes but not for the attacker
Oof. Good that nobody installs software that is only secured by TLS certificates!
I don’t even know what TLS certificates are.
Okay, the other comment was actually pretty funny. But this one’s a serious answer.
Transport Layer Security protocol is a way to share secrets. Basically, it’s the lock on your airport luggage. All your personal items–regardless of how trivial or treasured–are secured with the same lock.
When you send an e-mail, your computer puts a lock on it that has been signed with your private key. It’s sent to a recipient, who can unlock it with their own key. There’s a complicated exchange of keys and ciphers called a ‘handshake’ that happens when a website is loaded on your computer, or an e-mail is received. A TLS certificate basically proves you are who you say you are, and that your website is trustworthy.
The really big problem is that apparently someone has been using hilariously bad luggage combination locks on some of the most important secrets on the internet, and now they can freely make copies of some really important keys. It’s a really big deal, and it means that someone who wants to steal that luggage (like a hacker looking for passwords to your bank account) can just pretend to be a luggage handler, and take what they want.
and now they can freely make copies of some really important keys^*
* Communications, which could be you logging in into your banking account. The attacker would be able to see your banking password, for example. Or it could replace a software update your laptop is receiving with malware. A manipulated WLAN router in a cafe or an airport could do that.
This was the ELI5 version, and admittedly, network security isn’t my strong suit. Thank you for the correction.
Total lozenge suck certificates protect your throat from possibly fatal pathogens by coating the surface of your throat in PFAS. Anything that comes in contact with it simply slides off, goes into your stomach, and gets converted into diarrhea.
Is this the OG poem for your sprig?
Omg!!
Definitely not. This one doesn’t do poetry
That comment above is poetry.
Who?
Sprog.
Who’s sprog?
Lol this guy doesn’t know sprog.
It was a username on another site, a while ago. They wrote in poems. Nice stuff.
Someone has commandeered their name here on the fediverse; or so it seems.
Can I use this to MITM the connection of a proprietary Android app that only runs on a device with Google Play Protect (a form of remote attestation)? And then reverse engineer the API?
Assuming that the device hasn’t been updated yet, yeah, this is what it allows you to do.
If you connect your device to a ‘fake’ router that’s completely under your control, then when the device attempts to connect to its remote server, you pretend to be it, and provide a certificate signed by this ‘trusted’ authority. Device will accept it. Make another connection to the real remote server. Decrypt what the device sends you, and send it on to the remote server; it’ll believe that you’re the android device, and respond with a message that you can decrypt, store, reencrypt with your fake key, and send it to the device. Repeat.
You’ll only be able to impersonate the API until the keys are revoked by an update. That’s maybe not so useful. However, any other connection that can be MITM’d and include other personal information - your bank card details, say - can be read, too.
So this means, i shouldn’t use my old android anymore?
With my ‘security hat’ on, I’d have to say you shouldn’t use anything that’s no longer receiving updates. But that would create a lot of e-waste for no reason.
To see if your phone’s browser is still receiving updates, you can browse to:
https://emudhra.we-have-a-problem.com/
That has a grid showing whether your browser was willing to connect to sites using the compromised keys. If your browser is using its own cert style and still receiving updates, should be all green ticks. If so, then you can still use the phone for browsing internet. Be aware that using other apps on your phone (like eg. your email app) could be read easily by third parties, especially if you’re connected to unfamiliar wifi.
If it’s all red, maybe try another browser? Or relegate that device to being a dumb phone - switch off its data connection, phone calls only.
Depends. If the app uses cert pinning it will only trust the cert baked into it.
Okay, that’s fun and scary at the same time.
The article links to a webpage,
https://emudhra.we-have-a-problem.com/
That shows if your browser is still using those certs, and though it says Firefox has already updated, maybe it hasn’t reached mobile yet as it shows I’m using them all still.
I guess I won’t connect to anything important for a few days.
My Firefox mobile got green ✅
Maybe try manually updating through the app store
Mine showed red, but after updating it now shows all green
In app safari on Mlem got all greens.
What’s odd is that I have auto updates disabled for Firefox on my spare phone, and I still show green on everything. I don’t think it’s updated in a couple months now.
Firefox can push certificate revocation updates without having to push a new browser build
I think cert updates happen automatically on their own without the browser needing to be updated.
There are no entries in the certificate transparency logs for these intermediates in that period, indicating that CT-enforcing clients like Firefox, Chrome, Edge and Safari could not have been attacked.
what version are you on?
That one is on version 154.0, dated August.

Useful link, thanks.
Mobile Waterfox passes.
Interesting. I’m also using Waterfox and getting all red on my end.
Huh. I have version 1.2.8.1.
1.2.9 for me. Seems like I might have to revert to the older one.
is the post body having issues displaying? asking because this is way past the first time this season i’ve seen people not see it
It’s displaying fine for me, I think I was just scrolling quickly on my phone and didn’t notice that the https://emudhra.we-have-a-problem.com link in the body was different from the linked article. I saw a blockquote in the post body, and figured that the URL beneath the quote was a link to the article.
I’m using Firefox and that site says I’m good.
Update mobile Firefox it should be fixed now
Yep, my Firefox mobile hasn’t updated yet either, gonna see if there’s an update I can grab.
Uhh… Weird. In my phone (Android 15) both Firefox 158.0.1 and Brave 1.97.59 (Chromium 155.0.8059.85) connect to 6 of the 12 hosts.
But on my tablet (Android 10) I have the same versions of Firefox and Brave, and there they don’t connect to any of the hosts.
What can I do?
Odd my mobile Brave rejects all.
I’m getting “⚠️ Inconclusive (timed out)” on Firefox 👀
For mobile
- Vanadium 155.0.8059.84 (config 217) on GrapheneOS connects to
6/120/12. Last updated 2026-10-17 - Fennec 158.0.0 (build #1580020) connects to 12/12. Last updated 2026-10-14
- edited: after I hit ‘run again’ a couple times Vanadium went 0/12, so hurray. Didn’t make a difference to my dear Fennec though.
My Vanadium just refused all 12 connections. But maybe some of the DNS blocking or Suricata on my LAN might have helped.
Thanks, I tried harder and got the same result as you. Edited my comment above to reflect.
I just recently swapped to Fennec and it’s correctly getting 0/12. These updates seem a bit inconsistent.
- Vanadium 155.0.8059.84 (config 217) on GrapheneOS connects to
I’m on a 10/7 build and I’m vulnerable on mobile FireFox, as well.
Edit: updated to a 10/19 version, 158.0.1, and it’s still vulnerable.
Ironfox is all green for me.
Cromite is half red, half green.
So yeah, fuck Chromium’s monopoly.
Do you mean not connecting to anything? Because that would be the action if you considered this a threat
That’s… what I said?
I do consider this a threat. A root certificate being compromised is a big deal. Your web traffic goes across multiple devices before reaching its intended destination, and if any one of them are compromised they could successfully perform an invisible man in the middle attack of your browser/app keeps trusting those certificates.
Ssl is pretty useful, yeah, but those that were mass unlocked with a gimmick key were already very insecure and at this moment they are revoked. Either way, aren’t you supposed to be locked in now?
That only applies to applications and services that support remote certificate revocation.
Those certificates were still in use until Firefox offered another update this morning, but that’s just the browser. Every company and their little bastard love child wants you to use an app to connect to their services, how many of those apps support automatic certificate revocation?
Any app on your phone that doesn’t is now vulnerable to being compromised invisibly. A successful MITM attack looks like nothing at all. The attacker decrypts the traffic with the compromised certificate’s secret to snoop in on the secrets (like username and password) and re-encrypts it to send it forward so the destination server doesn’t know any different either.
Now that it’s public knowledge, I guarantee someone is trying to capitalize on it right now.
How certain are you that not a single switch between you and your bank’s website is fully secured?
Are you using a vpn/tor?
WDYM you’re still using them all?
You don’t have e any green ticks?
Brave Mobile is green ✅
At this early stage, the most immediate threat appears to be for those using VPNs, especially in countries with governments likely to maliciously intercept traffic.
So, all governments?
I’m confused, doesn’t a VPN help protect against mitm in public networks? Are you saying that governments might use this at VPN exit nodes? That actually makes sense
For VPNs to be vulnerable, the VPN provider’s internal traffic must flow through an MITM server before exiting the VPN provider’s internal network. VPN providers don’t have any specific weakness or flaw that would would make an MITM attack easier to execute, but it is definitely true that a VPN provider would be a high-value target for such an attacker, both because a large volume of traffic flows through the VPN provider, and also because people who use a VPN provider are more likely to be doing so because they are doing things that their government wouldn’t approve of.